AR/2026 · personal dossier

Abdiwali Ahmed Abdisalam — web application security

00

بِسْمِ اللَّهِ الرَّحْمَٰنِ الرَّحِيمِ

Abdiwali Ahmed Abdisalam

professional brief

Django / Python Developer

Web Application Security

mogadishu · somalia (work-from-anywhere)

Django/Python engineering and web-application security under one roof — building tools, breaking things responsibly, and teaching a generation of Somali learners to do the same.

continue to page 01 ↓

01

whoami_

Portrait of Abdiwali Ahmed Abdisalam
fig. 01 — operator, at desk [1]

Django/Python Developer and Web Application Security practitioner with a Bachelor's degree in Computer Science and ongoing Master's studies in Cybersecurity. Experienced in building web applications, security tools, reconnaissance automation, vulnerability assessment platforms, and hands-on cybersecurity training environments.

Combines software engineering knowledge with practical web security experience — with a particular focus on Django applications, APIs, authentication and authorization, web vulnerability assessment, security automation, and secure application development.

Built and deployed multiple independent software and cybersecurity projects — web security scanners, penetration-testing automation tools, JavaScript reconnaissance tooling, and interactive training platforms. Author of five technical books in Somali on cybersecurity, networking, SQL Injection, XSS, and Nmap.

field
django · python · web security
focus
recon · osint · vuln assessment · automation
record
2 advisories filed · 10 projects shipped
languages
somali · arabic · english
ARKANI § 01whoamip. 01
02

Findings_

vulnerability research
Abdiwali Ahmed Abdisalam — long-form field strip
fig. 02 — site of operations, wide view [2]

Responsible vulnerability research — real findings from real engagements, targets and identifying details redacted. Written up in English, with proof-of-concept evidence included.

critical
REPORT 001 CWE-639 · IDOR
found · 2025

IDOR — Broken Authentication on Communication Endpoints

Business-logic flaw · horizontal privilege escalation · PII disclosure

summary

An Insecure Direct Object Reference combined with a broken business-logic check exposed other customers' sensitive data. The "access token" in the request was format-checked only — never actually tied to the authenticated user's record.

discovery chain

  1. Recon. Downloaded every JS bundle on the target subdomains, hunting for API endpoints, base URLs, tokens, and query parameters.
  2. Signal. The JavaScript revealed a backend base URL. Frontend requests carried ?n=<uuid> and nt — described in-app as access tokens for the data.
  3. Hypothesis. Is n validated server-side, or merely required to look like a UUID?
  4. Proof. Requests with no token, an all-zero UUID, and a random UUID all returned 200 OK with full data. A non-UUID value returned 400 "Unable to validate communication." — format-only validation.
  5. Escalation. Reusing the same token against a different communication ID returned another customer's record — no valid token or auth required.

impact

Sensitive PII exposed cross-customer: customer names, holdings, a masked account identifier, and a full voting record — accessible with no authentication. Horizontal access is a proven primitive.

recommendation

Bind every token to the owning record and the authenticated user server-side, and authorize each object access against the session identity. Format validation is not authorization.
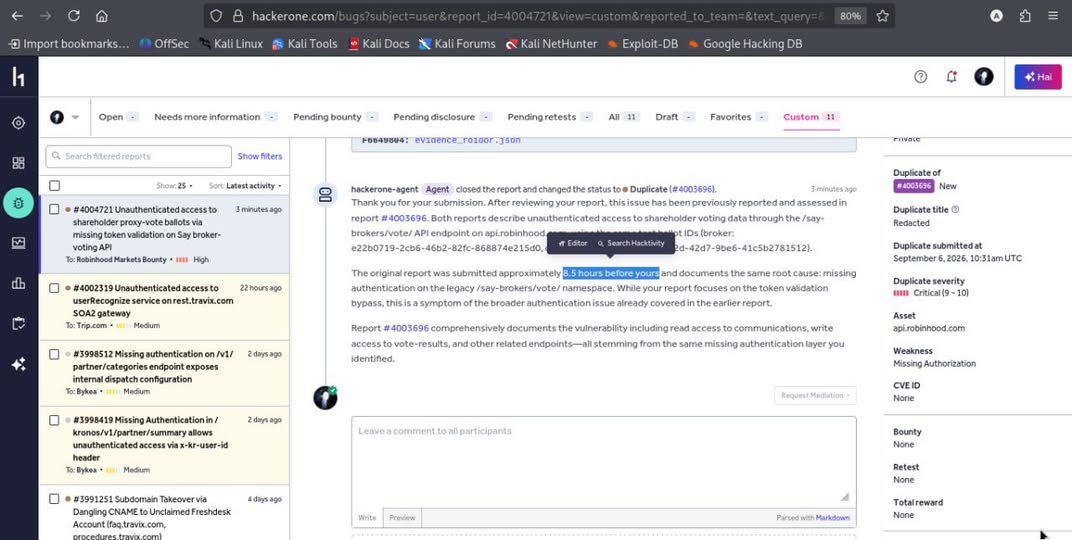
Proof of concept — IDOR: requests without a valid token returned 200 OK with full data
evidence — PoC: token-less requests → 200 OK
# 1 — no token
GET /api/communication?mid=0000...
HTTP/1.1 200 OK
{ "customer": "...", "holdings": "...",
  "voting_record": [ ... ] }

# 2 — invalid uuid → still OK
GET /api/communication?n=00000000-0000-0000-0000-000000000000
HTTP/1.1 200 OK

# 3 — non-uuid → rejected (format only)
GET /api/communication?n=not-a-uuid
HTTP/1.1 400 "Unable to validate communication."
high
REPORT 002 CWE-942 · CORS
found · 2025

CORS Misconfiguration — Credentialed Cross-Origin Access to Production API

Any *.target.com subdomain trusted · chainable with subdomain takeover

summary

The production API server trusts any subdomain of the target domain for credentialed cross-origin requests. A single weak link in the subdomain attack surface unlocks full authenticated API access.

observation

A request carrying a subdomain Origin made the server reflect it and grant credentials; external origins received a no-credential wildcard response. Trust is deliberately scoped to all subdomains.

attack chain

  1. Takeover. Find a dangling CNAME to a third-party service and claim the orphaned subdomain.
  2. Payload. Host malicious JavaScript on the controlled subdomain.
  3. Execute. The script makes credentialed cross-origin requests carrying the victim's cookies.
  4. Pivot. The origin is trusted → full API access with the victim's session.

recommendation

Replace wildcard subdomain trust with an explicit allowlist of production origins. Validate CNAME records, monitor for dangling DNS, and treat every subdomain as a security boundary.

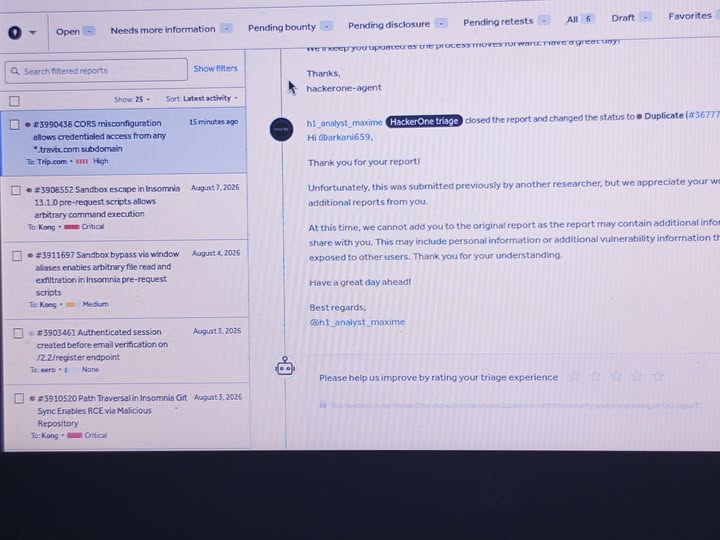
Proof of concept — CORS misconfiguration reflecting subdomain origins with credentials
evidence — PoC: subdomain origin + credentials reflected
# request with subdomain origin
POST /api/auth/login HTTP/1.1
Host: api.target.com
Origin: https://evil.target.com
Content-Type: application/json
{"username":"test","password":"test"}

# response
HTTP/1.1 200 OK
Access-Control-Allow-Origin: https://evil.target.com
Access-Control-Allow-Credentials: true

# external origin → wildcard, no credentials
Origin: https://attacker.com
Access-Control-Allow-Origin: *
ARKANI § 02findingsp. 02–03
03

Toolkit_

capabilities

Layered taxonomy — engineering, security, and operations disciplines, recorded as a technical index.

§ 3.1 — Programming & Web
python · javascript (ES6+) · html5 · css3 · django · mern stack · bootstrap
§ 3.2 — Backend & Databases
django · rest apis · mysql · mongodb
§ 3.3 — Cybersecurity
web app penetration testing · vulnerability assessment · exploitation · bug bounty methodologies · security testing · security reporting
§ 3.4 — Recon & OSINT
passive & active recon · subdomain enumeration · content discovery · cloud asset enumeration · subdomain takeover detection · crt.sh · alienvault · hackertarget
§ 3.5 — Security & Dev Tools
nmap · git · github · security header analysis · configuration analysis · automated pdf reporting
§ 3.6 — Cloud & Infrastructure
aws security fundamentals · secure deployment practices · linux
§ 3.7 — Networking
network scanning · defensive security techniques · ccna fundamentals
ARKANI § 03toolkitp. 04
04

Shipped_

selected work
04.1 SAHMIYE web pentesting & bug-bounty automation python · security automation
  • End-to-end automation framework covering the bug-bounty workflow — from reconnaissance through reporting.
  • Modules for passive/active recon, subdomain enumeration, content discovery, vulnerability discovery, subdomain-takeover detection, cloud asset enumeration, and network scanning.
  • Automated professional PDF security assessment reports.
open record →
04.2 BaareWeb web security scanning platform django · javascript · bootstrap
  • Web-based security scanning platform for identifying common web vulnerabilities and security misconfigurations.
  • Vulnerability detection and professional reporting.
  • Blends Django backend development with practical web-security concepts.
open record →
04.3 RaadraacJS javascript api & secret discovery tool javascript · web security
  • Recon tool that analyzes JavaScript files and URLs to uncover hidden API endpoints, exposed secrets and tokens, and the client-side attack surface.
  • Purpose-built for web penetration testing and bug-bounty reconnaissance.
open record →
04.4 SecureScope web security header analyzer security · web app security
  • Local-first security analyzer for HTTP, TLS, CORS, and CSP configurations.
  • Operates without user accounts or external services.
open record →
04.5 Web Pentesting Handbook interactive 16-chapter handbook ↗
04.6 SahalHadiye passive recon · target profiling ↗
04.7 Bakaaro POS mern · transactions · inventory ↗
04.8 Nmap — Bilow ilaa Dhamaad learn nmap in an interactive terminal ↗
04.9 Intelligent Chatbot django · nlp ↗
04.10 Student Management django · mysql ↗
ARKANI § 04shippedp. 05
05

Labs_

training platforms

Hands-on cybersecurity training platforms in Somali — practical vulnerability discovery and exploitation, built for self-hosted learning.

Abdiwali Ahmed Abdisalam — lab detail
fig. 03 — lab bench, close view [3]
20 rooms SomXSS Academy interactive xss training platform demo ↗
20 labs SomSQLi Platform locally hosted sql injection labs demo ↗
15 rooms SomJWT Academy jwt vulnerabilities & auth bypass github ↗
lab SomVuln Academy ssrf & xxe vulnerability training demo ↗
ctf flags SomPT Academy path traversal & idor practice labs github ↗
sim CyberOS browser-based ethical hacking simulation demo ↗
course CyberBaro & Muraajacda CCNA cybersecurity and networking learning platforms live ↗
ARKANI § 05labsp. 06
06

Publications_

books

Five Somali-language technical books on cybersecurity and networking education — written to lower the barrier for Somali-speaking learners.

  1. [1]

    Nmap in Somali

    network scanning
  2. [2]

    Fundamentals of Cybersecurity

    beginner guide
  3. [3]

    Networking Basics in 30 Days

    networking
  4. [4]

    SQL Injection — Techniques & Prevention

    web security
  5. [5]

    Cross-Site Scripting (XSS) — Vulnerabilities & Mitigation

    web security

↳ volumes distributed via the telegram channel.

ARKANI § 06publicationsp. 07
07

Record_

education & certifications

education

ongoing

Master's Degree in Cybersecurity

City University, Mogadishu, Somalia

threat modeling · vulnerability analysis · defensive security · incident response · malware analysis · encryption & cryptography · network security · web application security · security monitoring

2020–2024

Bachelor of Computer Science

University of Somalia (UNISO), Mogadishu, Somalia

software engineering, algorithms, data structures, networking, databases, and IT systems

2025

MERN Stack Development Training

City University, Mogadishu, Somalia

full-stack development with MongoDB, Express.js, React, and Node.js

2025

Web Penetration Testing

Self-directed — Udemy & TryHackMe

reconnaissance, scanning, exploitation, web application security testing, and vulnerability reporting

certifications

wiz

Bug Bounty Masterclass Certificate

modern bug bounty methodologies, vulnerability research, responsible disclosure, and practical web security

verify →
aws academy graduate

Cloud Security Foundations

aws architecture, cloud security fundamentals, and secure deployment practices

verify →
beidat academy

Cloud Computing Security

cloud security, threat modeling, and secure infrastructure management

verify →
udemy

Recon for Bug Bounty

reconnaissance methodologies for penetration testing and bug bounty research

verify →
ARKANI § 07recordp. 08
08

Correspondence_

open channels
now
master's in cybersecurity · building somali security education
interests
ethical hacking · ctf · open source · security education
references
available upon request